
Security Vulnerability Report Handling Rules
Version: V0.0.3
These rules take effect on July 22, 2026 and supersede all previous versions.
The Fygo Security Response Center may revise these rules as the business evolves and regulations change. Revised versions will be published in this document, with update notices posted on the forum, and will take effect on the date of publication. Vulnerability reports already submitted and under review will be assessed and rewarded under the version of the rules in effect when they were submitted.
The Fygo Security Response Center reserves the right of final interpretation of these rules.
1. Scope
This program covers:
-
Official production releases of FygoOS
-
Fygo-owned domains and services
-
Official apps and API endpoints
This program does not cover:
-
Legacy versions that are no longer maintained
-
Third-party plugins or components
-
Unofficially modified firmware
-
Third-party services not controlled by Fygo
-
Other application services running in users' privately deployed environments
2. Reward and Severity Criteria
Review Process
Rewards from the Fygo Security Response Center currently consist of report quality rewards and vulnerability or intelligence rewards. The reward program will continue to evolve based on industry practices and user needs. Standard rewards are paid in cash.
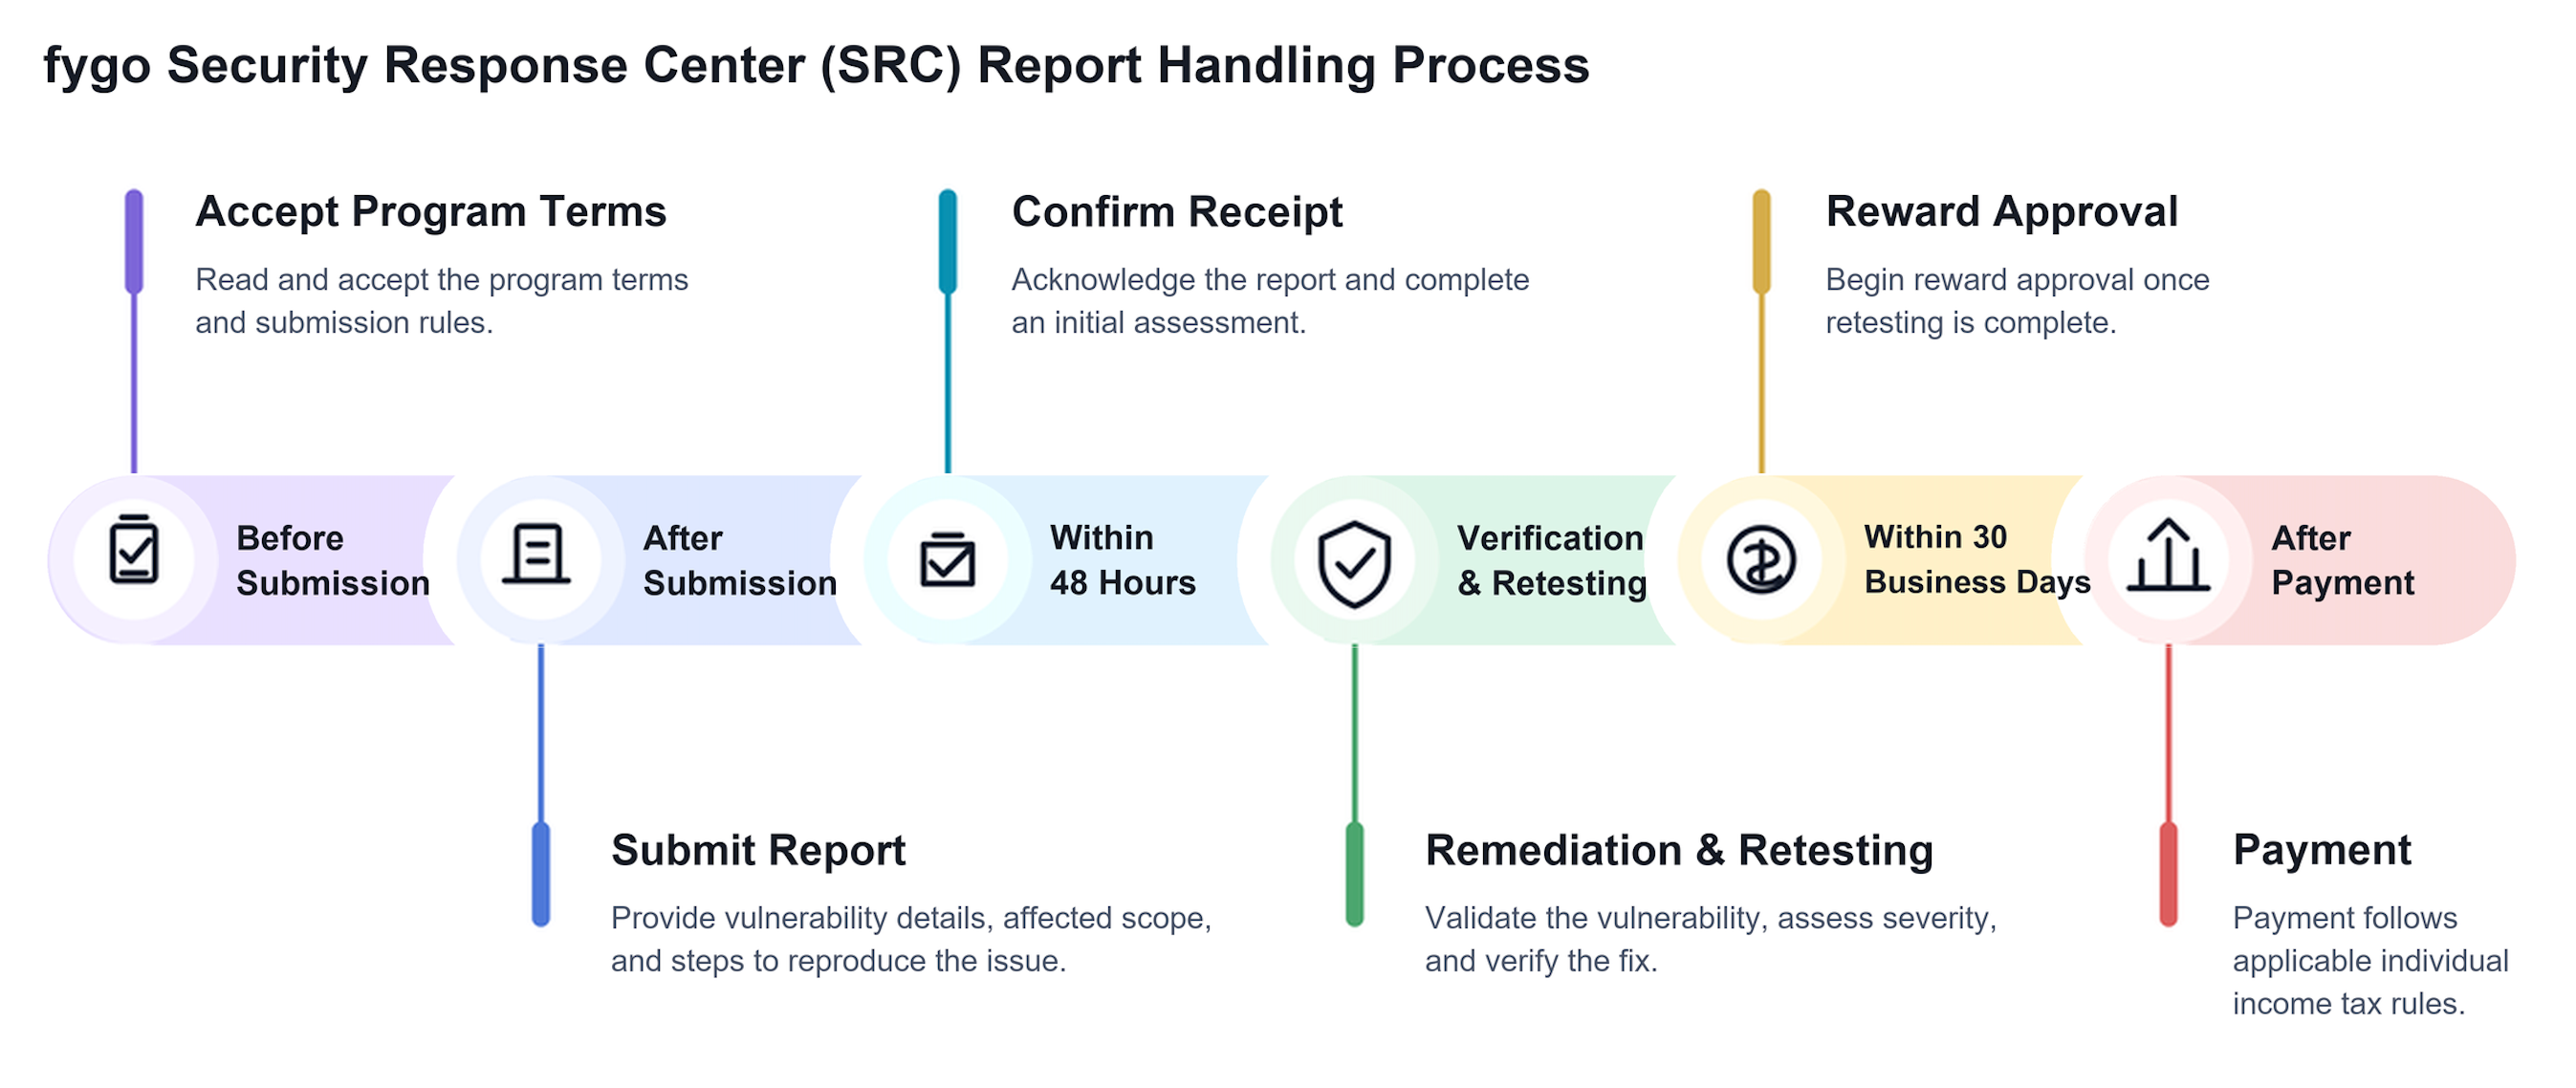
Security Report Reward Rules
The final severity and reward amount are determined by the Fygo security team based on a comprehensive assessment. Publicly disclosed vulnerabilities will be downgraded or excluded from consideration.
Vulnerability severity is classified into four levels: Critical, High, Medium, and Low.
Vulnerability / intelligence reward reference:
| Business Scope | Critical | High | Medium | Low |
|---|---|---|---|---|
| FygoOS operating system | $1,500-$4,500 | $350-$1,500 | $75-$350 | 0-$75 |
| Fygo-developed apps, FygoConnect, and more | $1,500-$3,000 | $300-$1,500 | $75-$300 | 0-$75 |
| Fygo Forum and other web services | $300-$750 | $120-$300 | $45-$120 | 0-$45 |
Maximum Vulnerability / Intelligence Rewards by Business Scope
Operating system: FygoOS - maximum reward of $ 4,500
Software and cloud services: Fygo-developed apps, FygoConnect, and more - maximum reward of $3,000
Web services: Fygo Forum and more - maximum reward of $750
3. Vulnerability / Intelligence Severity Assessment Criteria
1. Report Preparation Requirements
A complete and clear security report is essential for receiving a reward. It helps us locate the issue quickly and complete the review. The level of detail in a vulnerability report affects its final score. Security researchers must therefore include information such as the Vulnerability Title, Vulnerability Description, and Reproduction Steps in every report. Reports that omit this information will be excluded from consideration. For details, see the Vulnerability Report Writing Template.
-
Reports that are exceptionally well-structured, clear, and detailed, or that demonstrate an original exploitation approach, may receive an additional cash reward from the review team. We reserve the right of final interpretation of the rules governing additional cash rewards.
-
A vulnerability report must include:
-
Vulnerability Title: The vulnerability name, affected domain, vulnerability type, and other relevant information
-
Vulnerability Description: The entry point, relevant URL, parameters, app version, and other relevant information
-
Reproduction Steps: Step-by-step instructions for reproducing the vulnerability that demonstrate its impact and potential harm. Screenshots and written explanations of all key steps are required. See the report template for detailed requirements
-
Remediation: Actionable remediation recommendations, such as suggested code changes or protective measures
-
2. Detailed Vulnerability Severity Definitions
1) Critical Vulnerabilities
Security issues that, under the default configuration, may result in complete loss of control over a device, system, service instance, or core component, including but not limited to:
-
Obtaining the highest system privileges without authorization
-
Executing arbitrary code without authorization
-
Remotely taking control of a device or service instance
-
Bypassing authentication mechanisms and gaining uncontrolled access to core privileges
-
Obtaining core sensitive data from a device, system, or defined scope
Requirements
-
Reliably reproducible
-
Does not require social engineering
-
Does not depend on unofficial configurations or unconventional deployments
2) High-Severity Vulnerabilities
Issues that have a major impact on system security, data security, or the permission model but do not result in complete loss of control, including but not limited to:
-
Privilege escalation vulnerabilities
-
Unauthorized access to sensitive data
-
Access control failures in core features
-
Issues that may compromise multiple user accounts
3) Medium-Severity Vulnerabilities
Issues that may affect system or data security under certain conditions but are difficult to exploit or have a limited impact, including but not limited to:
-
Limited permission control flaws
-
Information disclosure under restricted conditions
-
Access control flaws that depend on specific environments
-
Security issues that require specific prerequisites to exploit
-
Privilege escalation vulnerabilities under restricted conditions
Notes
- The issue may affect user data or permissions but has significant exploitation prerequisites
4) Low-Severity Vulnerabilities
Issues with a limited and manageable impact on system security, including but not limited to:
-
Disclosure of low-sensitivity information
-
Logic issues with no direct impact on data security
-
Security flaws with no practical exploitation value
Notes
-
Does not involve core privileges or sensitive data
-
Does not affect control of the system
5) Excluded Reports
-
Vulnerabilities unrelated to Fygo's business
-
Vulnerabilities in third-party products that are not developed or operated by Fygo
-
Reports that provide insufficient detail
-
Vulnerabilities already known internally
-
Vulnerabilities that have been widely disclosed through public channels
6) Downgrading Factors
-
The issue only exists under a non-default configuration
-
The vulnerability requires authentication
-
The vulnerability cannot be reproduced reliably
-
Exploitation requires user interaction
-
The scope of impact is very limited
-
The issue has no practical business impact
-
Parts of the exploitation path duplicate those of another vulnerability
-
Exploitation requires stringent conditions
7) Special Notes
-
Vulnerability timeliness
-
If multiple security researchers submit the same vulnerability, the Fygo Security Response Center will reward the researcher who submitted the earliest detailed, authentic, and valid report. All other reports will be treated as duplicates and excluded from consideration
-
If a security researcher voluntarily asks us to disregard a vulnerability report and then resubmits it, another researcher may submit the same vulnerability before the new report is received. The original researcher assumes the resulting duplicate-report risk
-
-
Merging reports:
-
Multiple vulnerabilities that originate from the same underlying flaw, or that would all be resolved by fixing a single flaw
-
Multiple vulnerabilities that do not originate from the same underlying flaw but are of the same type within the same system or use similar exploitation methods
-
Unauthorized create, read, update, or delete operations in the same feature must be consolidated into one report and will be accepted as one vulnerability
-
Multiple vulnerabilities that must be exploited in sequence will be scored based on the maximum impact achievable through their combined exploitation
-
3. Detailed Intelligence Severity Definitions
1) Security Intelligence
-
Intelligence about attacks targeting FygoOS or related services
-
Vulnerability exploitation observed in real-world environments
-
Information about malicious scanning, exploitation tools, or attack scripts
-
Malware or attack samples targeting NAS devices
-
Potential attack trends that may affect the security of Fygo users
-
Key indicators of compromise for an affected server
-
Key evidence that a core business database has been downloaded, such as the database name or files
-
Key evidence of payment business logic exploitation or business process bypasses
-
Source links, network packet samples, or other key evidence of worm propagation, traffic hijacking, and similar activity
-
Key evidence of large-scale theft of sensitive user data, such as attack code or vulnerability exploitation tools
2) Business-Related Intelligence
-
Key evidence of organized abuse of Fygo product promotions or benefits
-
Key evidence of the disclosure of Fygo internal information or user data
-
Key evidence of payment fraud involving Fygo
3) Intelligence Severity Definitions
Critical Intelligence
- Threat intelligence involving a major impact on core business operations, systems, or office networks, or significant financial losses to the company
High-Severity Intelligence
- Threat intelligence involving a substantial impact on core business operations, systems, or office networks, or substantial financial losses to the company
Medium-Severity Intelligence
- Threat intelligence involving a moderate impact on core business operations, systems, or office networks, or moderate financial losses to the company
Low-Severity Intelligence
- Threat intelligence involving a minor impact on business operations, systems, or office networks
Valid Intelligence
To preserve the value and fairness of the intelligence reward program, threat intelligence must meet the following conditions:
-
The information is authentic and verifiable
-
The information has not been widely disclosed through public channels
-
The information is not already known to the Fygo security team through existing monitoring or telemetry systems
-
The information indicates a potential security impact on Fygo products, services, or users
When all the conditions above are met, the Fygo security team will assess the intelligence and may grant a reward based on its value, scope of impact, and actionability.
Invalid Intelligence
- Invalid intelligence is incorrect, meaningless, or cannot be investigated or acted upon based on the available information. Examples include:
-
False, fabricated, or artificially manufactured intelligence
-
QQ group numbers, traffic manipulation websites, or advertisements distributed by cybercrime groups that may be related to traffic manipulation or referral abuse but are submitted without detailed supporting evidence
-
Traffic manipulation by one or a small number of users resulting from issues unrelated to business rules
-
Intelligence that has already been discovered or is no longer valid
-
Intelligence that omits the attack path or attack method, or presents it unclearly or illogically
-
Intelligence involving a data leak must include at least 20 valid samples with traceable identity fields, such as order numbers, phone numbers, or national ID numbers. If evidence of data sales is discovered, the report must also include the seller's contact information, complete chat records, and payment method. Intelligence that does not meet these requirements will be excluded from consideration
-
4) Special Notes
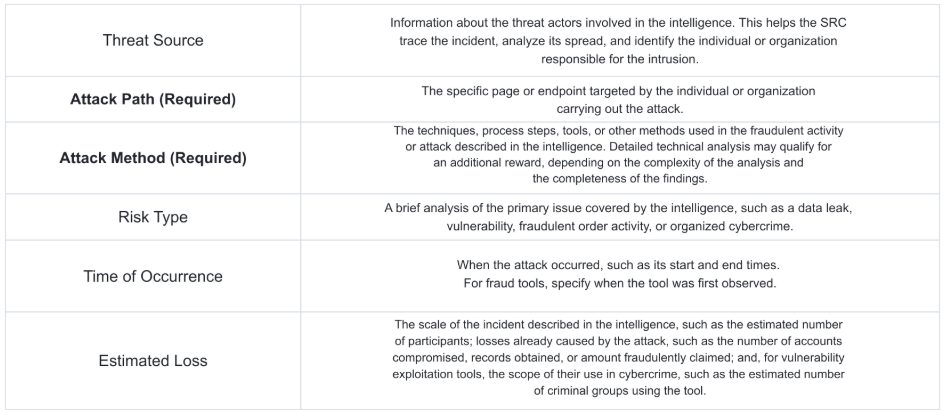
Completeness is an important factor in intelligence scoring. A threat intelligence submission must include the key evidence relevant to the reported scenario, including the threat source, attack path, attack method, risk type, time of occurrence, and estimated loss. See the report template for details.
4. Severity and Reward Notes
-
The final severity and reward amount are determined by the Fygo security team based on a comprehensive assessment
-
Only the first valid reporter of a vulnerability is eligible for a reward
-
Reports with exceptional quality, in-depth analysis, or remediation recommendations may receive an additional reward at our discretion
5. Handling AI-Generated Security Reports
As large language models become increasingly capable, using AI tools to assist with or automate vulnerability discovery has emerged as a new trend in security research. We have recently received some high-quality vulnerability reports for issues discovered with AI assistance. At the same time, we have also received many invalid reports that were not verified by a person, including false positives caused by AI hallucinations.
To allocate our limited review resources appropriately, allow the Fygo review team to focus on genuine vulnerabilities, and maintain a healthy community, we have updated these rules to establish submission standards for vulnerability reports discovered or generated with AI assistance:
AI use is encouraged: Fygo encourages security researchers to use AI tools to assist with or automate vulnerability discovery, improve discovery efficiency, and identify more potential risks.
Strict human verification: Vulnerability reports produced through AI-assisted or automated discovery must be verified by a person before submission. You must assess and reproduce the report's validity and impact and provide detailed human verification results in the report, including but not limited to:
-
A description of the vulnerability's impact
-
Detailed reproduction steps
-
A complete proof of concept (PoC)
-
Screenshots of key steps and results
-
A screen recording where necessary
Handling invalid reports: Reports generated directly by AI that have not been manually reproduced or do not include screenshots demonstrating valid verification results will be rejected by the Fygo Security Response Center without an explanation.
Handling repeated violations: If a security researcher submits more than three AI-generated reports without manually validating them, the Fygo Security Response Center will issue a warning. If a security researcher submits more than five such reports, the Fygo Security Response Center reserves the right to block the researcher from the Fygo Security Reward Program.
We recognize that AI is profoundly changing how security research is conducted and improving its efficiency. However, high-quality vulnerability reports still require human judgment and accountability. We ask all security researchers to uphold professional ethics and rigorous quality standards while benefiting from this technology, and to work with us to maintain a professional, efficient, and sustainable platform for vulnerability disclosure and communication.
4. Third-Party App Security
Some apps in the Fygo app ecosystem are provided by third-party developers. In principle, responsibility for their code and security maintenance rests with their developers.
To continuously improve ecosystem security, we will continue strengthening the review processes and listing requirements for third-party apps, including but not limited to:
-
Basic security reviews before listing
-
Standardized permission declarations
-
Risky behavior warning mechanisms
-
Improvements to vulnerability response and coordination processes
Principles for Handling Vulnerabilities in Third-Party Apps
-
In principle, Fygo does not provide cash rewards for vulnerabilities within third-party apps.
-
We continue to welcome vulnerability reports from security researchers concerning third-party apps.
-
If an app is verified to pose a security risk, we may take the following measures as appropriate:
-
Temporarily delist the app or restrict downloads
-
Publish a security risk advisory
-
Notify the developer to remediate the issue
-
Rewards and Assistance
For confirmed vulnerabilities in third-party apps:
-
The Fygo Security Response Center may help establish communication between the security researcher and the app developer;
-
If the third-party developer is willing to offer a reward or acknowledgment, Fygo will assist with communication and coordination;
-
Whether a reward is offered and the reward amount are determined solely by the app developer.
Security Responsibility
Responsibility for vulnerabilities in third-party apps rests with their developers. Fygo assumes no direct responsibility for defects in third-party code but will actively fulfill the security management and risk control responsibilities of the Fygo Security Response Center.
5. Final Interpretation
Vulnerability severity and final reward amounts are determined based on a comprehensive assessment of factors including the vulnerability's actual scope of impact, exploitability, effect under the default configuration, potential for exploitation at scale, and report quality.
The Fygo Security Response Center reserves the right of final interpretation of this program.